Web Gateway 1.2.2 · Public WebPKI
Is your TLS security stronger or weaker when deploying an SWG?
The answer depends on your web gateway's capabilities.
 Martin Stecher
November 21, 2026
One of the most critical parts of cybersecurity is our ability to trust HTTPS connections. Recent security incidents are a wake-up call to review how secure the TLS ecosystem actually is. What has changed over the last few decades? And what about our security tools? Do they improve our TLS security, or are they even putting us at higher risk in certain attack scenarios?
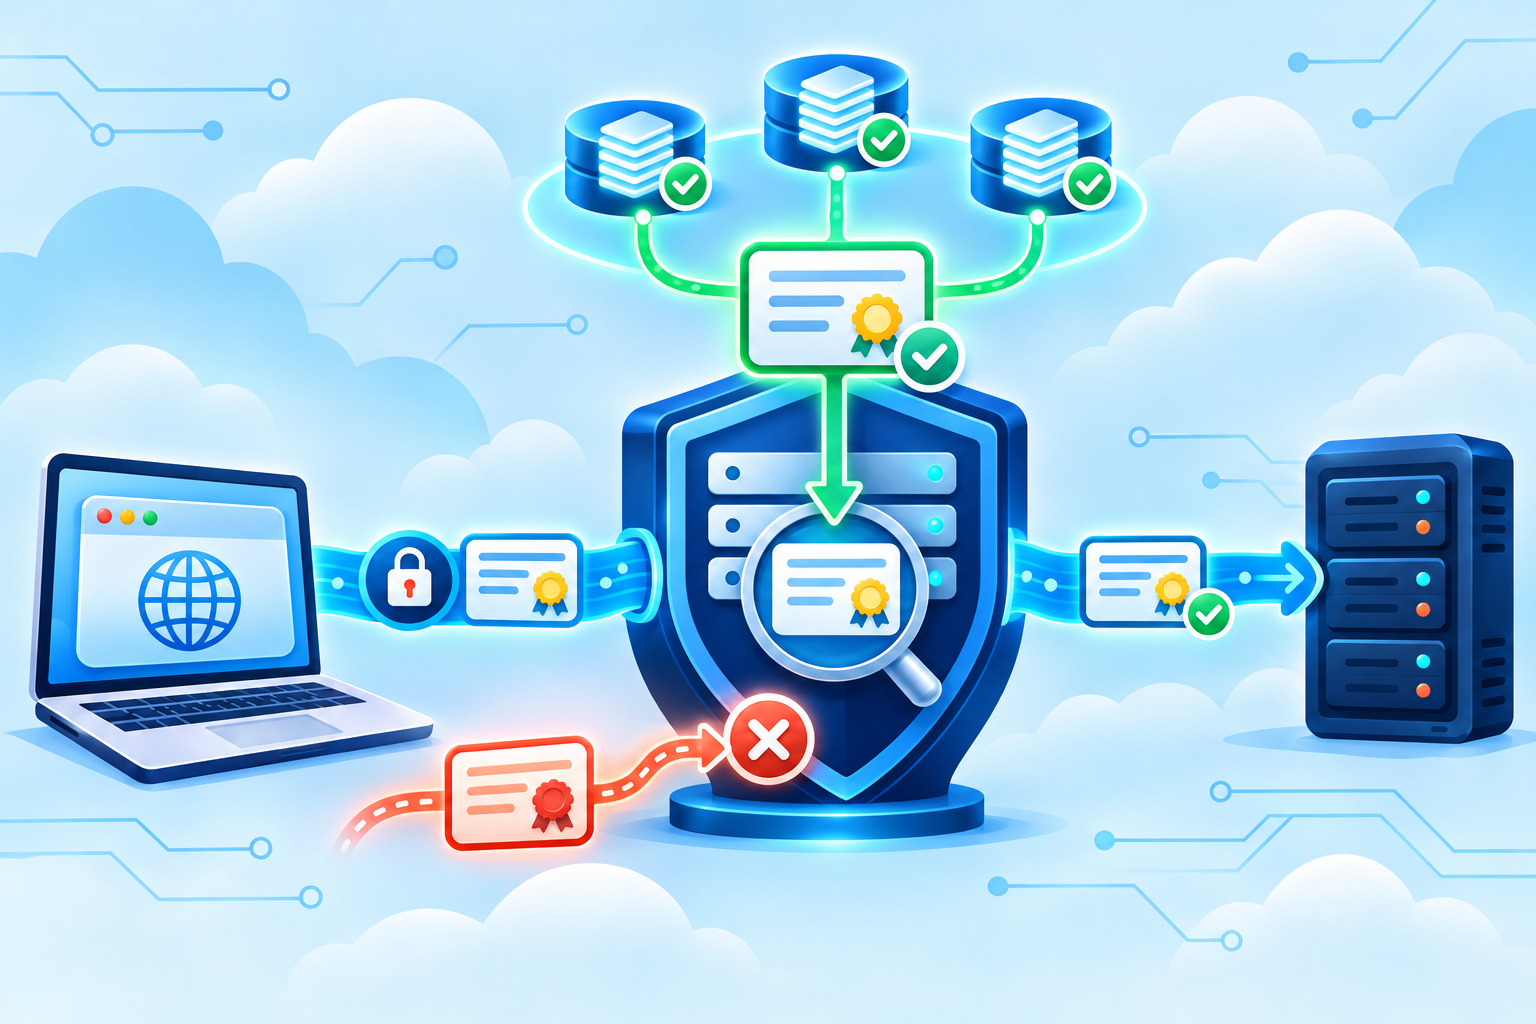
When a gateway terminates TLS, the browser no longer validates the web server certificate. The gateway does. Whether that makes you safer or less safe depends on how well the gateway does that job.
TL;DR
- Browser vendors have introduced important new TLS security controls over the last 10 years, but many vendors of Secure Web Gateway solutions do not think they need to participate in those initiatives.
- That approach is dangerous for the overall security ecosystem and even more so for customers running solutions without those security controls, because a browser cannot apply its enhanced protections to the origin certificate when operated behind a TLS-terminating forward proxy.
- If you deploy TLS content inspection and you are unsure whether your SWG product keeps up with these security needs, ask your vendor the three questions we list at the end.
The early days
TLS inspection and termination at the gateway level started about 25 years ago. That was a time when only a minority of websites offered HTTPS. TLS security relied much more on the user as the deciding factor: browsers presented details about the web certificate and expected the user to decide whether anomalies such as a name mismatch or an expired certificate were acceptable. Encountering a server whose certificate had expired was a normal part of the daily web experience, and the user had to understand the risk and decide whether to allow the connection.
This was when the first Secure Web Gateways (SWGs) appeared with TLS termination, installed as an approved man-in-the-middle in corporations to inspect HTTPS content against company security policies. The web server certificate was no longer visible to the end user; instead, the SWG decided whether the certificate on its upstream connection was valid. In many cases, the SWG could make a better security decision than the users in a corporation, with an administrator's policy deciding instead of less-trained end users: The SWG actually improved HTTPS security for the corporation!
Browsers also took over more of the certificate validation work. The user experience became simpler, with a lock symbol and, for a time, a green address bar indicating certificate status and type (DV, OV, or EV). If you would like to read more about the different certificate types, see our earlier blog article.
Both browsers and SWGs also checked for certificate revocation through Certificate Revocation Lists (CRLs) and the Online Certificate Status Protocol (OCSP). In those years, the policies in browsers and most SWG products were on par.
But things evolved on the browser side. From a user perspective, they became simpler and simpler. Experts are not always happy about that simplification because it takes extra effort for them to understand the details, but browsers made up for it by introducing new controls for good reasons. Let us explore what those reasons are, how those controls work, and why support for them is also important for an SWG!
Recent threats as a wake-up call
Let us recall two major issues in the TLS security ecosystem from recent weeks:
- Attackers compromised the authoritative DNS infrastructure of several country-code top-level domains, including
.gh,.sl, and.as, and were able to modify DNS records in those zones. They then passed domain validation and obtained publicly trusted HTTPS certificates for prominent Google domains and other organizations. The automated workflows and the fact that TLS security is built on top of DNS security allow this kind of attack whenever authoritative DNS infrastructure is compromised. Google describes the incident and its response in Chrome's Response to Recent ccTLD Registry Hijacks. - A widely accepted Root CA operator, eMudhra, certified several intermediate CA keys whose private values were so weak that they could be recovered from public information. An attacker who recovered the private key of one of the affected TLS intermediate CAs could use it to sign certificates for arbitrary server names that would chain to a trusted root. Mozilla documents the incident in Bug 2083449.
As severe as these “must-not-happen incidents” were, the industry could respond because it knows that these kinds of issues are possible and will happen from time to time. The important countermeasures are early detection, short exposure windows, and rapid revocation or distrust.
Let us see how those techniques have evolved and work today. We will come back to both incidents afterwards.
How revocation works today
As mentioned above, there was a time when OCSP was assumed to solve the problem: a browser or SWG queries the status of a certificate through a URL provided by the CA. But it turned out that live OCSP checking can be attacked as well and has latency, scalability, availability, and privacy problems. Soft-fail behavior also means that an attacker can block the OCSP request without blocking the TLS connection. Chrome disabled live OCSP checking in 2012, and Let's Encrypt stopped providing OCSP information for newly issued certificates in 2025. For the public web, live OCSP checking is now almost dead, even though OCSP stapling and specialist uses remain. Feisty Duck provides a good history in The Slow Death of OCSP.
We have always had Certificate Revocation Lists (CRLs), but having every client download all of them directly from all CAs is also a scalability problem.
The WebPKI ecosystem has therefore reduced the exposure of a compromised certificate by demanding that website certificates remain valid only for a relatively short time. At the time of this writing, newly issued website certificates can be valid for no more than 200 days. This will go down to 100 days from March 2027 and then to 47 days from March 2029. Shorter lifetimes do not replace revocation, but they limit how long a compromised certificate can be abused and also reduce how long revoked certificates need to remain in revocation data.
Instead of every browser downloading every CRL directly, browser vendors distribute purpose-built revocation data to their installed products through mechanisms such as CRLSet, OneCRL, and CRLite. These mechanisms allow them to react specifically to certificates and CAs that represent a threat. And that takes us to observability and Certificate Transparency enforcement.
Certificate Transparency
Public root programs require publicly trusted website certificates to be disclosed in public Certificate Transparency (CT) logs. Those logs are a great tool for domain owners to monitor whether certificates created for their domains all come from their own certificate creation workflows or whether an unknown certificate has appeared that may come from an attacker. Security providers also monitor the logs for their clients and hunt for general anomalies in certificate creation.
But what if an attacker is able to create a valid certificate (for example, with a compromised private CA key) but does not submit it to the CT logs?
The industry addressed that problem by having CT logs provide a Signed Certificate Timestamp (SCT) when they accept a certificate or precertificate for publication. The CA normally embeds those SCTs into the website certificate itself. Modern Chrome, Apple platforms including Safari, and Firefox enforce CT according to their individual policies. Those policies usually require valid SCTs from two or more recognized logs before a publicly trusted TLS connection can succeed.
An SCT does not prove that the certificate was issued legitimately. It proves that a recognized log has committed to publishing it. An attacker with a forged certificate therefore has two options: get it logged and become visible to everybody who monitors the logs, or skip the logs and have the certificate rejected by every CT-enforcing client.
Details about CT and how it works are well described on the CT community page.
Back to the two incidents
The ccTLD hijack certificates were properly issued and properly logged. CT enforcement did not and could not block them, because no certificate check can tell that the DNS validation behind a certificate was compromised. But CT made the issuance visible: Google used the logs to identify further affected organizations, Chrome blocked the unauthorized certificates through CRLSets, and the issuing CAs revoked them for everybody else. CT did not prevent the attack, but it made the response possible.
For the eMudhra intermediates, the direct protection was distrust. Once the weak keys were known, browsers distributed that decision through their update mechanisms, and certificates under those keys were rejected no matter which SCTs they carried.
Now imagine an attacker had discovered the eMudhra weakness months before security researchers found it. Getting SCTs for a forged certificate would have put it into public logs, where domain owners and security providers would have spotted it. So the attacker would rather create an unlogged certificate and present it only to clients that are known not to enforce CT. A modern browser would reject that certificate. A TLS-inspecting SWG without CT enforcement would happily accept it.
So where is the security problem?
A browser with the best CT enforcement policy cannot protect you when it is behind an SWG that terminates the TLS connection. The browser sees a website certificate signed by the CA that the SWG controls for its downstream connections. That internal CA trusted within the corporation is not itself a problem, even though the replacement certificate does not include public SCTs. The downstream leg between browser and SWG is under the corporation's own security control.
The problem is that the browser does not see the original certificate of the web server behind the SWG at all. It cannot check its SCTs, cannot match its issuer against its own distrust data, and cannot apply the current validity limits. The SWG's upstream side is hidden from the browser, so the browser cannot help.
It is the role of the SWG to enforce these controls for its upstream connection!
If the SWG does not participate in CT enforcement, there are three major problems:
- A problem for the overall ecosystem: a TLS-inspecting gateway without CT enforcement creates a detection blind spot. An attacker can selectively present it with an unlogged certificate that browsers would reject, leaving neither a public CT record nor a local security alert. With enforcement in place, the certificate is blocked and creates an incident that the operator can investigate and, where appropriate, report to the community.
- The biggest security problem arises for the company deploying such an SWG: in the scenario above, the attacker can stay under the radar for a very long time and fool non-enforcing SWGs. Nothing is in place to protect the company or even to make the attack visible so that countermeasures can be taken.
- A problem for your incident response: after incidents like the two in this article, the CT logs show which certificates were issued, and your access logs show which of the affected sites your users reached. With CT enforcement, that is the complete picture, because no unlogged certificate could have passed your gateway. Without it, you can never rule out that an unlogged certificate passed your other checks in the past, and you cannot give a reliable answer to the question “Were we affected?”
What did Cloud Fellows do?
We believe that, as an SSE vendor, it is our duty to participate in TLS security in a similar way to browsers today. Only if all user agents and gateways that terminate public TLS connections follow the same fundamental security practices can we secure the ecosystem as a whole. And only then can we really secure our customers.
Therefore, Cloud Fellows' Web Gateway implements these security controls as part of its TLS forward-proxy deployments:
- Maximum certificate validity: Enforcement of the agreed maximum validity periods for public website certificates, including their scheduled reductions.
- Managed certificate distrust: A signed
CertDistrustdatabase, maintained by us and downloaded regularly, that blocks public intermediates recorded in CCADB as revoked or whose issuer was revoked, plus the keys and certificates we distrust in response to incidents, such as the compromised eMudhra intermediate keys. It can block root CAs and individual server certificates as well. - Certificate Transparency enforcement: Enforcement of a published, combined CT policy designed to be at least as strict as the requirements of Chrome, Firefox, and Apple. This relies on the
CTRegistry, which we assemble centrally and which all installed Web Gateway nodes download regularly.
These checks apply to public website certificates, exactly where the browser would have checked them itself. Certificates of your internal enterprise PKI remain under your own trust policy.
With our version 1.2.2 release, these controls work together to close the security gap. We are happy to support you as a customer in trying the solution, potentially also as an upstream proxy hop in front of your existing solution as a stop-gap control point. And we are happy to partner with other vendors to achieve the same level of protection across the industry.
This brings browsers and SWGs back on par with their TLS security controls.
Questions to ask your SWG vendor
If you are unsure whether your current solution addresses these problems, ask your SWG or SSE vendor the following questions:
- When intermediate certificates such as eMudhra's compromised intermediates are revoked, how long does it take you to update your distrust data, and do my installed SWG instances update automatically?
- Does your SWG enforce the same reduction in maximum web server certificate validity as modern browsers and the WebPKI ecosystem?
- Does your SWG participate in the Certificate Transparency ecosystem and enforce a published SCT policy? How does the policy work, and how is its CT log list kept up to date?